 By First Compliance
Sanctions, PEP Screening, and UBO Compliance in UAE 2026: Navigating Geopolitical Risks and New Enforcement
Sanctions, PEP Screening, and UBO Compliance in UAE 2026: Navigating Geopolitical Risks and New Enforcement
In June 2026, the Central Bank of the UAE fined a foreign bank branch AED 20 million and personally fined its Head of Compliance AED 300,000, in the same investigation, for failures across anti-money laundering, counter-terrorist financing, and sanctions controls. That single action tells you where 2026 enforcement is headed: institutions and the individuals responsible for their compliance frameworks are now targeted together.
If your business operates in Dubai or anywhere in the UAE, this is the year effective PEP and sanctions screening in Dubai stops being a documentation exercise and becomes a test of whether your controls actually work. The UAE’s next FATF Mutual Evaluation, under the stricter 5th Round Methodology, had its onsite visit in June 2026, and it measures real-world outcomes rather than policies sitting in a drawer. At First Compliance, we build AML and due diligence software for UAE businesses navigating exactly this shift, and this guide breaks down what sanctions, PEP, and UBO compliance actually require heading into the rest of the year.
Why enforcement got sharper in 2026:
Three things changed at once, and together they explain the pressure UAE businesses are feeling right now.
Federal Decree-Law No. 10 of 2025 raised the ceiling on penalties: administrative fines for AML/CFT violations by licensed financial institutions now range from AED 5 million to AED 100 million, with criminal sanctions and imprisonment possible in cases of wilful non-compliance or systemic failure. The April 2026 CBUAE guidance package built on this by formalising proliferation financing as a standalone risk category every institution must assess independently.
CBUAE enforcement moved from institutional fines to personal liability: the AED 20 million penalty mentioned above came with a separate AED 300,000 fine against the bank’s MLRO for failing to meet the responsibilities of the role. This follows a May 2025 case where a branch manager was personally fined AED 500,000 and permanently banned from the UAE financial sector over an AED 200 million sanctions failure. In 2025 alone, CBUAE issued over AED 370 million in AML/CFT fines. The pattern is now established: the institution and the person accountable for the framework are both on the hook.
The FATF 5th Round Mutual Evaluation tests outcomes, not paperwork: the UAE’s national AML/CFT/CPF Committee reported in June 2026 that money laundering cases handled by law enforcement rose nearly 46 per cent year on year, with frozen assets reaching AED 150 million and FIU information requests up 20.7 per cent. Assessors will be looking for evidence that beneficial ownership transparency, sanctions implementation, and cross-border cooperation produce measurable results, not just written procedures.
What sanctions screening actually covers:
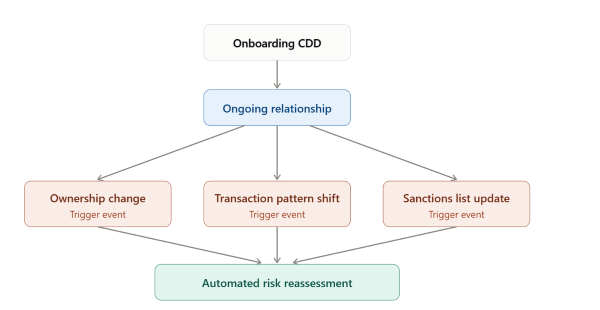
Sanctions screening checks whether a customer, director, UBO, or connected party appears on the UAE Local Terrorist List, the UN Consolidated Sanctions List, or other applicable regimes such as OFAC and EU lists. Regulated entities must screen at defined touchpoints:
- Before onboarding: to prevent a sanctioned individual or entity from entering the relationship in the first place.
- Immediately after list updates: screening must happen without delay to meet freezing obligations under the UAE’s Targeted Financial Sanctions regime.
- During periodic KYC reviews: to catch changes in a customer’s risk profile over time.
This is where the biggest gap shows up. A client can pass screening clean on Monday and appear on a sanctions list by Tuesday after a geopolitical event. Point-in-time checks alone leave that gap open, which is exactly why ongoing monitoring, not a one-time check, is what regulators and effective PEP and sanctions screening in Dubai now require.
PEP screening and the risk tier most businesses miss:
Being a politically exposed person is not itself a crime, but it does trigger Enhanced Due Diligence. Regulators typically classify PEPs into four risk tiers based on the seniority and reach of their position. Most compliance programmes screen the PEP directly and stop there, missing Tier 4: relatives and close associates.
RCAs are the blind spot: a corrupt official rarely places illicit funds in their own name. Funds move through a spouse’s, child’s, or associate’s account instead, so screening relatives and close associates carries the same weight as screening the politician. Getting this wrong is one of the most common findings in CBUAE enforcement actions, and it’s a core reason PEP and sanctions screening in Dubai has to go beyond a single-name check.
A practical tip worth knowing: the biggest operational pain point in screening isn’t missed matches; it’s false positives, where a system flags an innocent customer because they share a name with a sanctioned individual. Matching on date of birth and country alongside name, and applying fuzzy logic to catch spelling variants, cuts down false positives without weakening the check itself.
UBO compliance: the register regulators now cross-check:
Under Cabinet Decision No. 109 of 2023, UAE corporate entities must maintain an accurate, complete register of ultimate beneficial owners, with penalties for non-compliance set out in Cabinet Decision No. 132 of 2023. Identifying UBOs is a core part of Customer Due Diligence, and screening the UBO against sanctions and PEP lists is mandatory, not optional. False or misleading UBO information can now trigger criminal as well as administrative sanctions.
By 2026, UBO compliance isn’t a standalone registry task. It sits inside the same AML architecture as sanctions and PEP screening, and regulators expect all three to work together as one system rather than three separate checklists.
Sanctions, PEP, and UBO checks at a glance:
|
Check |
What it verifies |
When required |
UAE legal basis |
|
Sanctions screening |
Match against UN, OFAC, and UAE Local Terrorist List |
Onboarding, list updates, periodic review |
Federal Decree-Law No. 10 of 2025, TFS regime |
|
PEP screening |
Political exposure, including relatives and close associates |
Onboarding and ongoing monitoring |
Federal Decree-Law No. 10 of 2025, CBUAE guidance |
|
UBO verification |
Identity and screening status of beneficial owners |
Onboarding and register updates |
Cabinet Decision No. 109 & 132 of 2023 |
How First Compliance supports screening in a shifting risk landscape:
Geopolitical risk moves faster than manual review can keep up with. A client that was clean last quarter can be added to a watchlist overnight following a sanctions package, a change in government, or a new adverse media report. This is the core reason regulators, and the FATF evaluation itself, are pushing UAE businesses toward continuous monitoring instead of point-in-time checks.
First Compliance is built around that reality. Our platform runs real-time monitoring integrated with hundreds of global sanction lists, so new matches surface automatically rather than waiting for the next manual review cycle. AI-powered screening covers sanctions, PEPs, and adverse media in one pass, eKYC with real-time face verification simplifies onboarding, and dynamic workflows adapt as UAE regulations change. For businesses preparing for the FATF Mutual Evaluation, having documented, audit-ready evidence of ongoing PEP and sanctions screening in Dubai is exactly the kind of outcome-based proof assessors are looking for.
Getting ahead of the 2026 enforcement curve:
The direction of UAE compliance in 2026 is clear: heavier penalties, personal accountability for compliance officers, and an evaluation framework that rewards evidence over paperwork. Businesses that treat sanctions, PEP, and UBO checks as one connected, continuously monitored system will be far better positioned than those still relying on manual, point-in-time reviews.
If your current process still depends on quarterly spreadsheet checks, now is the time to close that gap. Schedule a free demo with First Compliance to see how real-time PEP and sanctions screening in Dubai, backed by hundreds of global watchlists, fits into your existing workflow.
Frequently Asked Questions
Can I still do business with a PEP?
Yes, generally. Being a PEP is not a crime on its own. It requires Enhanced Due Diligence, including closer scrutiny of the source of funds and ongoing monitoring, rather than automatic refusal of the relationship.
How often does sanctions screening need to happen in the UAE?
At onboarding, immediately following any update to the UAE Local Terrorist List or UN Consolidated List, and during periodic KYC reviews. Real-time monitoring closes the gap between list updates and your next scheduled review.
What happens if my UBO register is inaccurate?
Regulators can impose fines under Cabinet Decision No. 132 of 2023, and providing false or misleading UBO information can lead to criminal sanctions in addition to administrative penalties.
Why does 2026 feel stricter than previous years?
Federal Decree-Law No. 10 of 2025 raised penalty ceilings to AED 100 million, CBUAE has begun fining individual compliance officers alongside institutions, and the FATF’s 5th Round Mutual Evaluation grades real enforcement outcomes rather than written policy.
What's the single biggest gap in most compliance programmes?
Screening the PEP but not their relatives and close associates, and treating sanctions screening as a one-time onboarding check rather than an ongoing process.