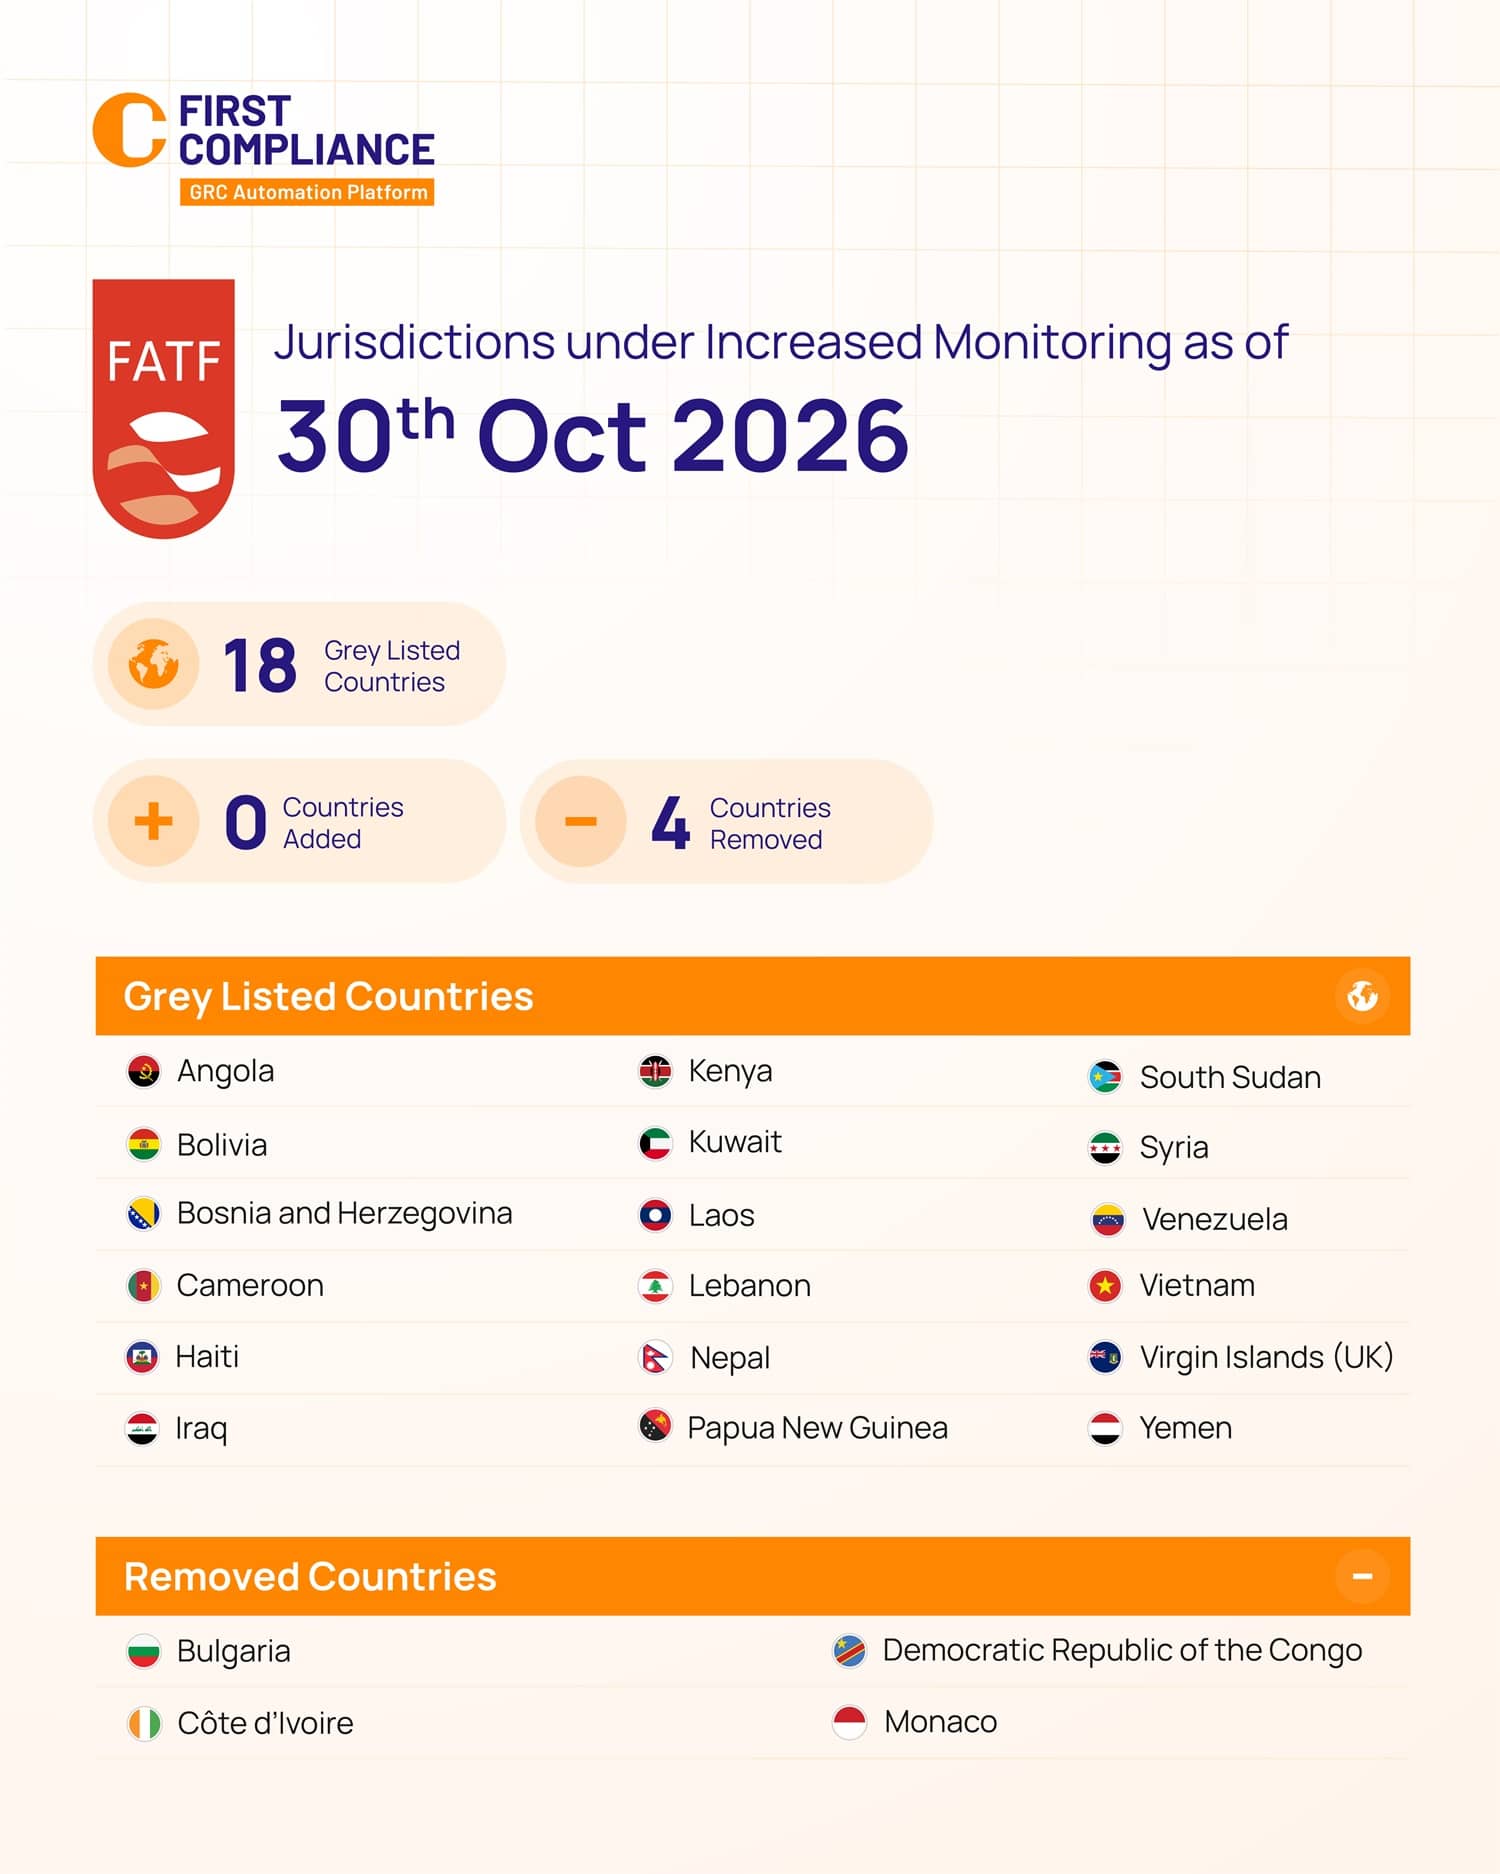
On 30 October 2026, the FATF removed Bulgaria, Côte d’Ivoire, the Democratic Republic of the Congo (DRC) and Monaco from its list of jurisdictions under increased monitoring, and added none. A policy update alone is not enough: unless the country tables inside your onboarding, screening and monitoring systems change too, your controls will keep scoring customers against the old list. This guide covers what changed and how to update each system.
What changed on the FATF grey list in October 2026
- Added: None
- Removed: Bulgaria, Côte d’Ivoire, Democratic Republic of the Congo (DRC) and Monaco
- Total under increased monitoring: 18
- Call-for-action list: No change
FATF grey list as of 30 October 2026
- Angola
- Bolivia
- Bosnia and Herzegovina
- Cameroon
- Haiti
- Iraq
- Kenya
- Kuwait
- Lao People’s Democratic Republic
- Lebanon
- Nepal
- Papua New Guinea
- South Sudan
- Syria
- Venezuela
- Vietnam
- Virgin Islands (UK)
- Yemen
FATF blacklist as of 30 October 2026
- Democratic People’s Republic of Korea (North Korea)
- Iran
- Myanmar
Why system configuration matters
Most compliance failures after a list change are not policy failures. They happen because a country risk table in one system was updated while another was not, leaving onboarding, screening and monitoring out of step. Regulators expect firms to show when each control changed and that it changed everywhere.
System update checklist after the October 2026 FATF update
| System | What to update | Evidence to keep |
| Customer risk assessment | Review weighting for Bulgaria, Côte d’Ivoire, Democratic Republic of the Congo and Monaco | Methodology version, effective date, approver |
| Customer onboarding (KYC/KYB) | Review EDD questions and source-of-funds checks tied to the delisted countries | Updated workflow configuration |
| Sanctions and PEP screening | Confirm country lists and any jurisdiction-based rules | Screening configuration log |
| Transaction monitoring | Review high-risk corridor rules for the delisted countries; tune thresholds | Rule change log, test results |
| Periodic review | Bring forward reviews for customers whose rating changed | Re-assessment report |
| Regulatory reporting | Check HRC/HRCA triggers (UAE) or local equivalents if the blacklist changed | Report register |
Review Existing Geographic Risk Classification
Updating the country risk table does not automatically change the risk ratings of existing customers unless a bulk reassessment is performed. Following the October 2026 update, identify customers, beneficial owners and counterparties linked to Bulgaria, Côte d’Ivoire, the Democratic Republic of the Congo and Monaco. Review their existing risk classifications and determine whether any adjustments are warranted based on the revised FATF status and your organisation’s broader risk assessment.
Keep an audit trail
Record who approved the change, when it took effect in each system, how many customers were re-rated, and what action followed. That record is what an inspector or auditor will ask for.
FAQs on the FATF grey list update, October 2026
Which countries were added to the FATF grey list in October 2026?
None. No countries were added to the FATF grey list at the Plenary that concluded on 30 October 2026.
Which countries were removed?
DRC, Monaco, Bulgaria, and Côte d’Ivoire were removed after completing their FATF action plans and passing on-site visits.
Do I need to update my AML software after every FATF update?
Yes. FATF lists change three times a year, and country risk tables in onboarding, risk scoring, screening and monitoring should all be updated together.
Does a grey list change automatically re-rate existing customers?
Only if your system supports bulk re-scoring. Otherwise, run a look-back and recalculate affected customers’ risk ratings.
What evidence should we keep?
The approval, effective date per system, number of customers re-rated, and resulting EDD or reports.
Keep every system in step with the FATF lists
First Compliance brings customer risk assessment, onboarding, screening, transaction monitoring and reporting into one platform with a full audit trail.